📌 Learn the most important network infrastructure design considerations, equipment selection, and how to build a stable and scalable network.
Principled enterprise network design, smart equipment selection, and step-by-step implementation are the keys to building a stable, secure, and scalable infrastructure.
What Is an Enterprise Network and Why Does Design Matter?
An enterprise network is the communication backbone of any modern business. It connects all devices, users, servers, and services within an organization and provides a platform for data exchange, resource sharing, and running applications. Enterprise network design goes beyond purchasing a few hardware devices — it is a strategic process that lays the foundations for efficiency, security, and the organization's future growth.
- High efficiency and productivity: Ensures smooth information flow by minimizing delays and downtime.
- Proactive security: Protects critical organizational assets by implementing security layers from the start.
- Flexibility and scalability: Enables growth and adaptation to changing business needs without requiring fundamental redesign.
- Cost reduction: By preventing costly failures and optimizing resource usage.
Key Principles of Enterprise Network Design
Enterprise network design is based on principles that every successful architecture must follow. Consider these as your roadmap:
1. Flexibility and Scalability: Designing for the Future
Organizations are constantly changing and growing. Network needs also evolve with the increase in users, opening new branches, and using cloud services. An ideal network must be able to grow and adapt to these changes.
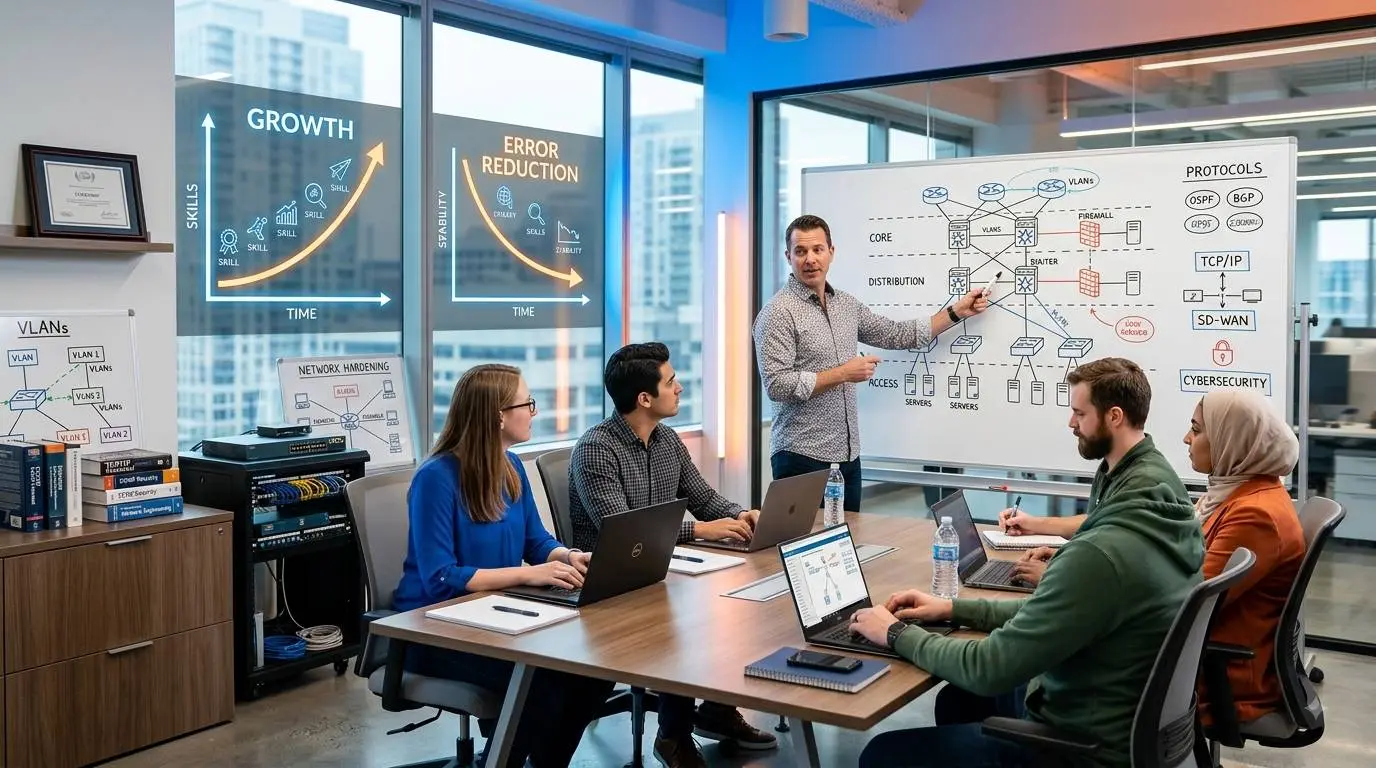
To achieve this goal, design the network in a layered manner (such as access, distribution, and core layers) so that each layer can be independently expanded. Also, choose equipment that supports diverse protocols and technologies and makes upgrades easy. For example, planning for extra bandwidth in the initial design prevents bottlenecks in the future.
2. Redundancy and High Availability
Network downtime for any reason can cause irreparable damage to the business. Therefore, designing a network that continues to operate even with the failure of one or more components is critical. This principle is known as "High Availability."
- Using two core switches in Active/Standby mode with HSRP or VRRP protocol so that if one fails, the other takes over quickly.
- Using multiple communication paths between network layers.
- Using dynamic routing protocols like OSPF that automatically find alternative routes when a path fails.
3. Security-First Design
Security should not be added as an extra layer after network implementation but must be integral to the network design from the start. A "security-first" approach means implementing security measures as part of the core architecture.
- Network Segmentation: Using VLANs and separate subnets, isolate traffic between different organizational departments (e.g., finance, marketing, guest) so that a breach in one area does not grant access to others.
- Zero Trust Implementation: Do not trust any user or device by default, and perform re-authentication for each access attempt.
- Firewalls and Intrusion Prevention Systems (IPS): For controlling incoming and outgoing network traffic.
- Role-Based Access Control (RBAC): Limit access to network equipment based on users' roles in the organization.
Choosing the Right Equipment and Technologies
Selecting network equipment is one of the most critical decisions in the design process. This choice should be based on the organization's needs, budget, and vision.
- Routers, switches, and firewalls: Form the core of the network. Access, distribution, and core layer switches should be selected based on throughput and required capabilities. Next-generation firewalls (NGFW) can provide much higher security than traditional models.
- Wireless equipment: For wireless communications, using WLAN controllers that centralize the management and security of access points is highly effective.
- Emerging technologies: Given the growth of cloud usage and remote work, implementing solutions like SD-WAN for intelligent management of communications between offices and using VPNs for secure remote user connections is essential.
Enterprise Network Implementation Steps
After design and equipment selection, it is time for systematic network implementation.
1. Documentation and Network Map Preparation
Before any action, prepare a complete and accurate map (both physical and logical) of the network to be implemented. This documentation will include network topology, device configurations, IP addressing ranges, and VLANs. A good map makes future troubleshooting and expansion much easier.
2. IP Addressing and VLAN Design
A structured plan for IP addressing and creating VLANs simplifies network management. Create a separate subnet for each department, device, or function (such as management, VoIP, user VLAN, and server VLAN).
3. Configuration, Testing, and Monitoring
After launching the equipment, thoroughly test the network. Ensure that routing, redundancy, and security rules are working correctly. After launch, continuous monitoring of the network to identify and resolve potential issues and optimize performance is essential.
Summary
Designing and implementing a successful enterprise network requires a systemic perspective and adherence to engineered principles such as flexibility, redundancy, and security. By following these principles and choosing the right equipment, you can create a stable and reliable infrastructure for your organization that not only meets current needs but also provides a suitable platform for future growth and innovation.
Frequently Asked Questions
Although all principles are critical, "security" and "redundancy" are typically prioritized higher, because an insecure or unstable network can lead to disaster for a business. Security must be considered from the start in design, and redundancy also ensures the network continues to operate when problems occur.
In three-layer design, the network is divided into three separate sections (access, distribution, and core). The core layer handles high-speed data transfer, the distribution layer applies policies and security, and the access layer is the connection point for users and devices. Two-layer design merges the distribution and core layers, which is more suitable for smaller networks but offers less scalability.
VLANs (Virtual Local Area Networks) allow you to divide a single physical network into multiple logical networks. This increases security (isolating traffic between different departments), improves performance (reducing broadcast domains), and simplifies network management.